A VPN normally sends all of your internet traffic through its encrypted tunnel. That's the point: everything is protected. But sometimes you want an exception. Your banking app refuses to work over a VPN. Your printer disappears from the network. A streaming app shows the wrong country. A work tool only works from your home IP address.
Split tunneling is the feature that handles those exceptions. It lets you decide which traffic goes through the VPN and which goes straight to the internet. Here's how it works, the different types, when it's worth using, and the risks to understand before you turn it on.
How VPN split tunneling works
Without split tunneling, a VPN creates one route for everything. Every app and every request goes into the encrypted tunnel, out through the VPN server, and on to the internet. Websites see the VPN server's IP address, and your internet provider sees only encrypted traffic going to one server.
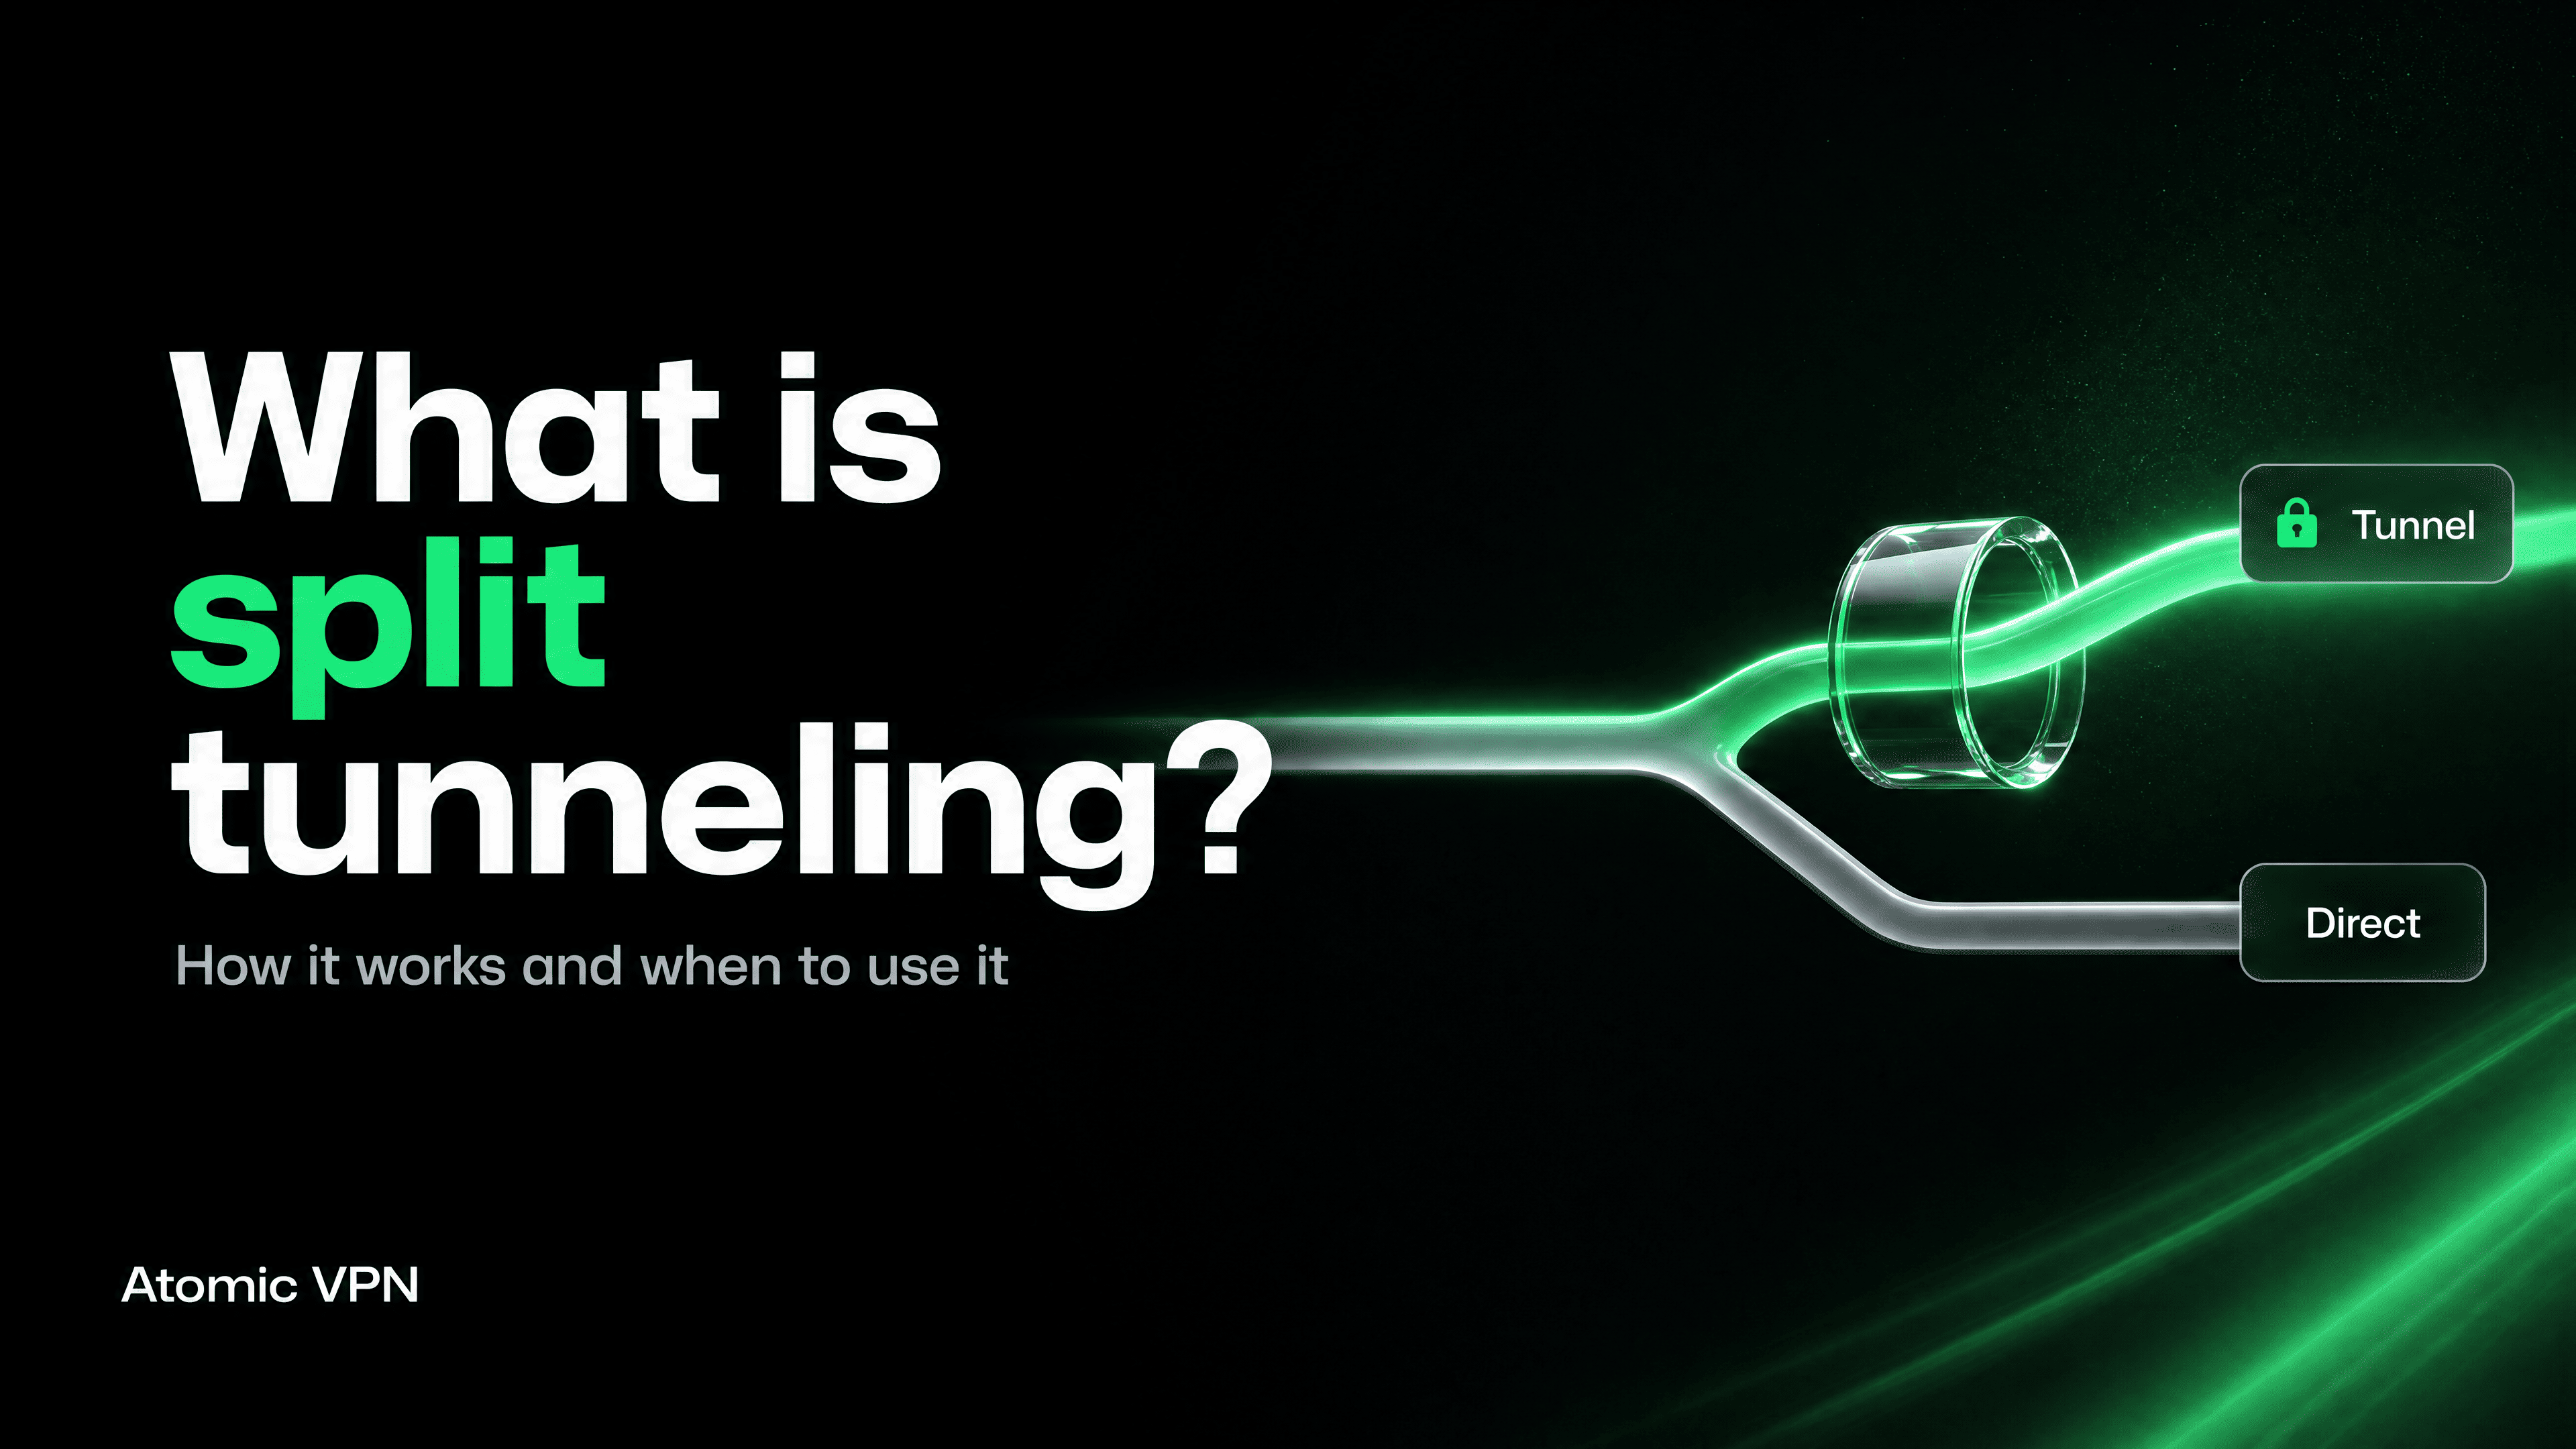
With split tunneling, the VPN app installs two routes:
- The tunnel route, for traffic you want protected. It's encrypted and exits from the VPN server.
- The direct route, for traffic you exclude. It goes out through your normal internet connection, from your real IP address, exactly as if the VPN were off.
Your device decides which route each connection takes based on the rules you set: by app, by website or IP address, or by type of traffic.
Types and modes of split tunneling
App-based split tunneling is the most common in consumer VPN apps. You pick apps from a list. On Android, this works through the system's VPN framework, which lets VPN apps include or exclude specific apps.
URL or IP-based split tunneling routes traffic by destination. It's more precise but harder to maintain, because large services use many IP addresses that change over time.
Inverse split tunneling flips the default. In inverse (or "include") mode, only the apps you pick use the VPN and everything else goes direct. In standard "exclude" mode, everything uses the VPN except what you pick. Exclude mode is safer for everyday use: if you forget about an app, it stays protected. Inverse mode fits a narrow job, such as protecting one app.
When split tunneling is useful
- Banking and payment apps. Some banks flag or block VPN IP addresses. Excluding the banking app lets it connect from your real address while the rest of your traffic stays protected.
- Local devices. Printers, network drives, smart TVs, Chromecast and AirPlay often become unreachable when all traffic goes through a VPN, because your device stops seeing the local network. Excluding local traffic fixes it.
- Streaming and local content. Watch a local service from your real location while other apps stay in the VPN, or the other way around.
- Gaming. Route the game directly for the lowest latency, while your browser and chat stay protected.
- Work tools. Companies often split traffic so video calls and cloud apps go direct, while internal systems go through the corporate VPN. Microsoft publishes guidance for sending Microsoft 365 traffic outside the corporate tunnel for this reason.
- Getting around a local block. In Spain, for example, some legitimate sites go offline during LaLiga matches because of IP blocking. Sending only the affected traffic through a VPN keeps everything else on your normal connection. See our guide to LaLiga blocks in Spain.
- Saving bandwidth. Large downloads or updates from trusted sources don't need to go through the VPN.
The risks and trade-offs
Split tunneling is a convenience feature, and every exception is a gap in your protection. Know what you're giving up:
- Excluded traffic isn't encrypted by the VPN. Your internet provider, the Wi-Fi owner, or anyone on a public network sees it the same way they would without a VPN. HTTPS still protects page content, but not which services you connect to.
- Excluded apps reveal your real IP address and location.
- DNS can leak. If the VPN isn't careful about DNS, lookups for excluded or even included traffic can go to your normal DNS server. Run a DNS leak test after setting up split tunneling.
- Browsers are tricky. If a browser is excluded, every site in it goes direct, including ones you'd want protected.
- On public Wi-Fi, keep exclusions to a minimum. Café, hotel and airport networks are where the tunnel matters most.
- Work devices. Corporate split tunneling is set by your IT team for a reason. Don't change it on a managed device.
A good rule: use exclude mode, exclude only what breaks, and review the list now and then.
Which devices support split tunneling?
How to set up split tunneling
The exact steps depend on the VPN app, but the flow is almost always the same:
- Open the VPN app's Settings.
- Find Split tunneling (sometimes under Advanced or Connection).
- Choose the mode: exclude apps (everything uses the VPN except selected apps) or include apps, also called inverse (only selected apps use the VPN).
- Add the apps, sites or IP addresses.
- Reconnect the VPN.
- Test: check your IP address in an included app and an excluded app. They should differ. Then run a DNS leak test.
Split tunneling vs. a kill switch
These two features pull in opposite directions, so it's worth understanding how they interact.
- A kill switch blocks traffic if the VPN connection drops, so nothing leaks outside the tunnel.
- Split tunneling deliberately lets some traffic go outside the tunnel.
How they interact depends on the VPN app. A system-level kill switch blocks all traffic on the device when the tunnel drops, which can cut excluded apps off too. Other apps let excluded apps keep using your normal connection. Check how your VPN handles it, and remember that excluded apps are never protected by the tunnel.
Split tunneling in Atomic VPN
Split tunneling is coming to Atomic VPN. Until it ships, Atomic VPN protects all of your traffic on the device, which is the safest default. When split tunneling arrives, it will be included on every plan.
What you get today:
- WireGuard by default, about 890 Mbps on a 1 Gbps line with 0.2-second reconnects, plus OpenVPN over TCP 443 for restrictive networks. See WireGuard vs OpenVPN.
- DNS inside the tunnel, with IPv6 blocked outside it by default.
- Router setup that covers every device on your home network without using a device slot.
- No activity logs, RAM-only servers and an independently audited no-log policy.
- $2 a month on the yearly plan, 5 devices, 88+ countries.
Apps for Windows and macOS are available now. iOS and Android apps are on the way.
FAQ
What is split tunneling in a VPN?
It's a feature that sends some of your traffic through the encrypted VPN tunnel and lets the rest use your normal internet connection. You choose which apps, sites or addresses go where.
Is split tunneling safe?
It's safe for the traffic that stays in the tunnel. Traffic you exclude isn't protected by the VPN, so exclude only what you need to, and avoid exclusions on public Wi-Fi.
Should I turn split tunneling on or off?
Leave it off unless something breaks with the VPN, such as a banking app, a printer or a local device. Then exclude just that app or device.
What is inverse split tunneling?
It's the reverse of standard split tunneling: only the apps or addresses you choose go through the VPN, and everything else connects directly. It suits protecting one app. For everyday use, exclude mode is safer, because anything you forget stays protected.
Does split tunneling make my VPN faster?
It can. Traffic you exclude skips the VPN server, which frees up bandwidth and lowers latency for those apps. Traffic in the tunnel runs at the same speed as before.
Can I use split tunneling on iPhone?
Usually not in consumer VPN apps. iOS offers per-app VPN mainly on devices managed by an organization. Android, Windows and many macOS VPN apps support it.
Does split tunneling cause DNS leaks?
It can, if the VPN handles DNS poorly. Run a DNS leak test after setting it up to make sure lookups for tunneled traffic go through the VPN.
What's the difference between split tunneling and a kill switch?
A kill switch blocks traffic when the VPN drops. Split tunneling lets chosen traffic bypass the VPN on purpose. Excluded apps are never protected by the tunnel, and how they behave when it drops depends on the VPN app.